Expose Hidden Liabilities Before You Inherit Them
In modern Corporate Development and Mergers & Acquisitions (M&A), the technology stack of the target company is one of the greatest sources of hidden liability. Traditional IT due diligence relies on questionnaires, interviews, and reviewing the target’s current real-time dashboard alerts.
But what if the target company was compromised six months ago, and the threat actor is lying dormant, waiting for the acquisition to connect the target’s network to your enterprise?
Real-time security tools don’t consider what already happened. That is the critical blind spot in M&A cyber due diligence — and the question no questionnaire can answer: are we about to acquire a breach?
The TensorGuard M&A Solution
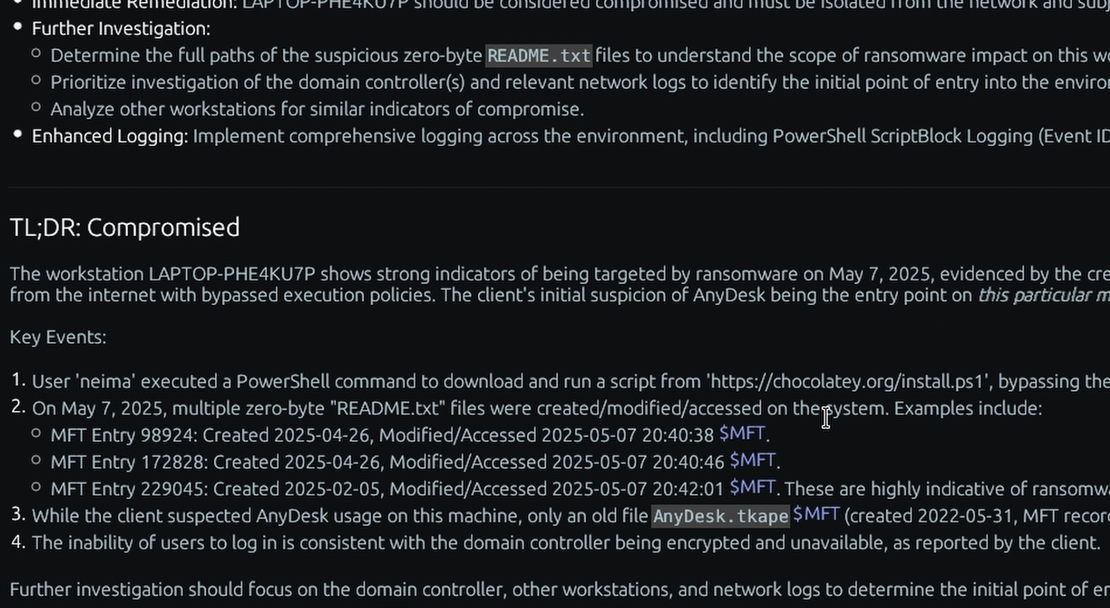
TensorGuard provides evidence-backed confidence during the critical due diligence window. We deploy a lightweight, read-only forensic agent across the target’s fleet to pull years of historical ground truth.
TensorGuard’s semantic analysis processes gigabytes of deep forensic artifacts—such as the $MFT, Amcache, and Windows Event Logs (.evtx)—across the entire target organization, delivering human-validatable findings.
Discover Historical Intrusions
Identify dormant threats and prior breaches that pre-date or completely bypassed the target company’s existing EDR and anti-virus software.
Validate The Security Posture
Don’t just take their word for it. Ensure that the target company’s network hygiene matches their answers on your M&A compliance questionnaires. Easily query the fleet in plain language: “Show me all devices where a USB drive was connected in the last 72 hours.”
Rapid, Quiet Deployment
M&A timelines are tight, and secrecy is often paramount. TensorGuard’s assessment takes minutes, not the weeks traditionally required by a manual Incident Response retainer.
High-Impact Payoff
Even a 1% price/terms adjustment on a $100M deal ($1M) dwarfs the cost of a fleet-wide TensorGuard sweep. Know exactly what you are buying before you sign.